PHP remains one of the most popular programming languages worldwide, powering a vast portion of web applications, corporate portals, and e-commerce platforms. However, due to its widespread adoption, servers running outdated PHP versions or applications with insecure configurations have become frequent targets for cybercriminals. Neglecting maintenance and postponing security updates represent severe risks that can compromise any organization’s stability, confidentiality, and reputation.
This article provides a detailed analysis of the primary security issues associated with PHP, the operational risks stemming from unpatched vulnerabilities, and how proactive infrastructure management is essential to keep digital environments fully secure.
The Threat Landscape in PHP Applications and Servers
As the language evolves, older PHP versions reach End of Life (EOL) and lose official community support. Once a version enters EOL, newly discovered security flaws are no longer patched by the original ecosystem, leaving servers exposed to automated exploitation by malicious actors.
Failing to apply security patches creates critical entry points that facilitate cyber intrusions, compromising databases, intercepting sensitive customer data, and disrupting core business operations.
Key Vulnerabilities and Risks of Outdated PHP
Understanding the risks threatening an IT infrastructure is the first step toward strengthening corporate defenses. Common threats in insecure PHP environments include:
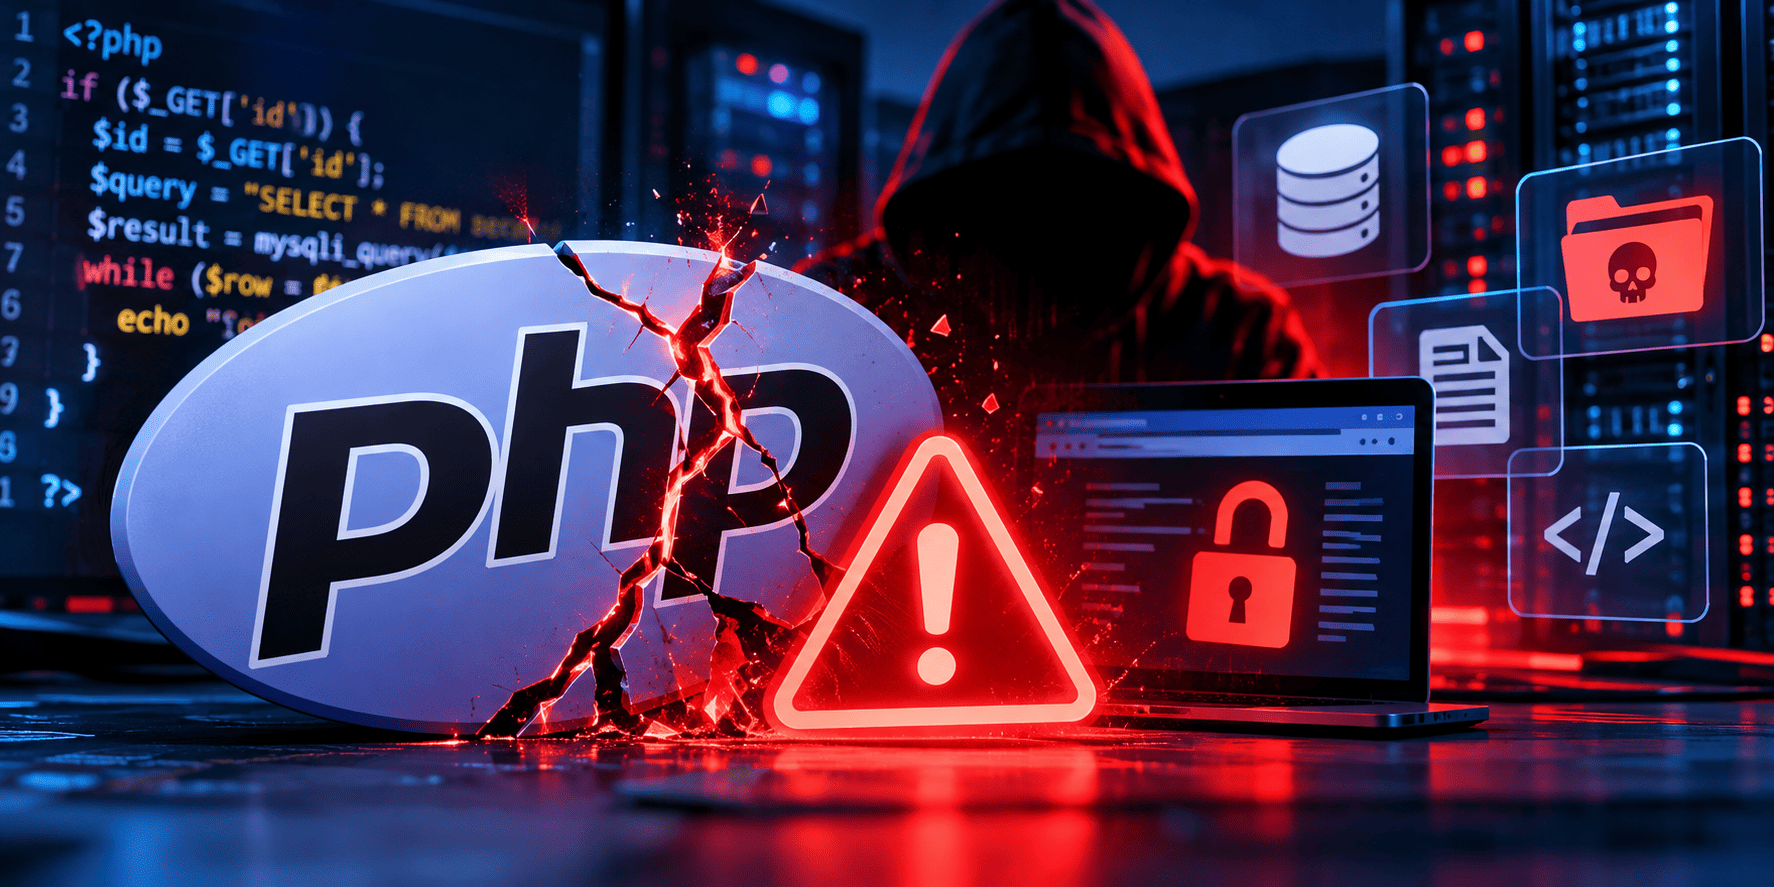
- Remote Code Execution (RCE): One of the most severe vulnerabilities, allowing attackers to execute arbitrary commands on the server and gain full system control.
- SQL Injection (SQLi): Occurs when improperly sanitized user inputs allow database query manipulation, leading to unauthorized data extraction or destruction.
- Cross-Site Scripting (XSS): Injects malicious scripts into web pages affecting end users, potentially stealing access credentials or session tokens.
- Local/Remote File Inclusion (LFI/RFI): Enables unauthorized reading of operating system files or the execution of malicious external scripts on the server.
- Malware Injection and Defacement: Injects malicious code into application source code to spread spam, exfiltrate data, or deploy ransomware.
Practical Business Impacts
PHP security issues go beyond technical inconveniences; they directly impact an organization’s financial health and strategic standing:
- Operational Downtime: Unavailability of critical systems resulting in immediate revenue loss and productivity drop.
- Regulatory Fines and Non-Compliance: Data breaches caused by known unpatched flaws can trigger severe penalties under data protection regulations.
- Brand Reputation Damage: Erosion of customer and partner trust following public disclosure of security incidents.
Best Practices for PHP Security and Risk Mitigation
Protecting digital environments against intrusions and mitigating PHP risks requires a multi-layered defense strategy:
- Maintain Regular Updates: Keep PHP updated to active, fully supported versions with the latest security patches.
- Deploy Web Application Firewalls (WAF): Inspect HTTP traffic to block common attack vectors before they reach application servers.
- Server Hardening & Secure Configuration: Disable dangerous functions in
php.ini(such asexec,system, andshell_exec) and enforce strict file permissions. - Continuous Monitoring & Vulnerability Scanning: Conduct regular security audits and monitor system logs to identify anomalous behavior.
How SERVICEINFO can help
Maintaining a fully secure and up-to-date IT infrastructure demands continuous oversight, specialized expertise, and a proactive stance against emerging cyber threats. For SERVICEINFO clients, information security is always the highest priority. Our engineering team works continuously and preventively to monitor environments, apply security patches, and mitigate vulnerabilities across PHP applications and corporate servers.
If you are already a SERVICEINFO client, you can enjoy full peace of mind knowing that our IT team works around the clock to ensure your infrastructure remains protected, updated, and performing at its best. That is one of the core advantages of partnering with SERVICEINFO: we take proactive measures before vulnerabilities turn into business risks, always delivering top-tier security, reliability, and excellence.
Looking to secure your corporate IT infrastructure with industry-leading practices? Contact the SERVICEINFO expert team today to explore our managed solutions.